> For the complete documentation index, see [llms.txt](https://docs.digibee.com/documentation/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.digibee.com/documentation/resources/best-practices/oauth2-integration-model-with-digibee.md).
# OAuth2 integration model with Digibee
Learn how to implement an OAuth2-based integration model to securely and efficiently authenticate and authorize connections.
This document presents an implementation model for the OAuth2 flow used for authentication and authorization in integrations carried out on the Digibee Integration Platform. The goal is to ensure secure access to protected APIs using access tokens and refresh tokens when applicable.
You will learn the standard implementation pattern of the OAuth2 authentication flow on Digibee, including:
* Credential generation steps
* Token retrieval
* Token refresh
* Credential removal
{% hint style="info" %}
**Important notes:**
* The pipeline must be configured with at least two simultaneous executions (Digibee Execution Config) to ensure the mechanism works correctly, since it performs a self-call to generate the token.
* The OAuth2 flow follows the `client_credentials` authorization grant, suitable for system-to-system integrations without human interaction.
* Token refresh is performed automatically before expiration, ensuring a valid token is always available for use.
{% endhint %}
## **Architecture**
### **Overview**
Diagram:
{% @mermaid/diagram content="flowchart LR
A\[External system] --> B\[OAuth2 Pipeline]
B --> C\[Credential creation]
C --> D\[Access token retrieval]
D --> E\[Token refresh]
E --> F\[Credential deletion]" %}
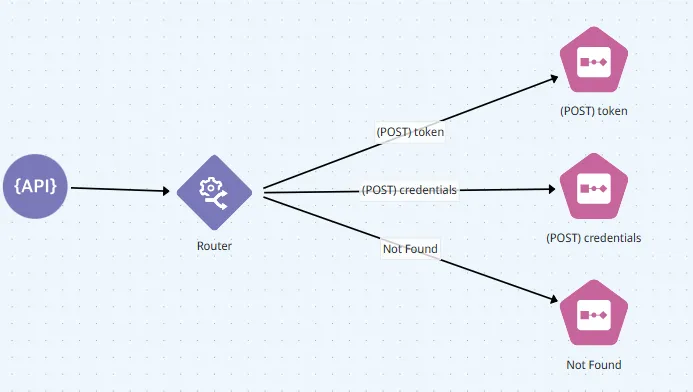
Pipeline:
### **Description**
* The pipelines implement a complete OAuth2 authentication flow, enabling:
* Credential creation
* Access token retrieval
* Token refresh
* Credential removal
* The responsible pipeline can be triggered for the initial token generation, token refresh, or credential management, depending on the input parameters.
* This mechanism can be reused by other business pipelines via event calls, APIs, or encapsulation in capsules.
### **Detailed flow**
1. **Credential generation**
* Creates a `clientId` and `clientSecret` pair for future authentications.
2. **Token retrieval**
* Generates the access token (`access_token`) and the `refresh_token`.
3. **Token refresh**
* Renews the access token using the `refresh_token` before it expires.
4. **Credential removal**
* Deletes the credentials (`clientId`) from the authentication system.
### **Payloads**
#### **1. Credential generation**
Request:
```json
{
"partnerId": "TestSystem",
"executionType": "create",
"apikey": "..."
}
```
Response:
```json
{
"clientId": "clientId",
"clientSecret": "clientSecret"
}
```
#### **2. Token retrieval**
Request:
```json
{
"password": "clientSecret",
"grant_type": "client_credentials",
"username": "clientId"
}
```
Response:
```json
{
"token_type": "Bearer",
"expires_in": 3600000,
"ext_expires_in": 3600000,
"access_token": "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9...",
"refresh_token": "eyJhbGciOiJIUzUxMiIsInR5cCI6IkpXVCJ9..."
}
```
#### **3. Token refresh**
Request:
```json
{
"grant_type": "refresh_token",
"refresh_token": "eyJhbGciOiJIUzUxMiIsInR5cCI6IkpXVCJ9..."
}
```
Response:
```json
{
"token_type": "Bearer",
"expires_in": 3600000,
"ext_expires_in": 3600000,
"access_token": "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9...",
"refresh_token": "eyJhbGciOiJIUzUxMiIsInR5cCI6IkpXVCJ9..."
}
```
#### **4. Credential removal**
Request:
```json
{
"clientId": "clientId",
"executionType": "delete",
"apikey": "..."
}
```
Response:
```json
{
"code": 200,
"message": "Success when deleting client credentials for the clientId: clientId"
}
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.digibee.com/documentation/resources/best-practices/oauth2-integration-model-with-digibee.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.